Every exposure. One action plan.

The Armada Platform continuously tests and defends your internet edge, internal network and AI usage, then turns every finding into a short list of fixes ranked by business impact.

Start the day with what changed.

New exposures waiting for review, priority exposures by severity, open findings and recent activity, on one screen. When nothing changed overnight, it says so.
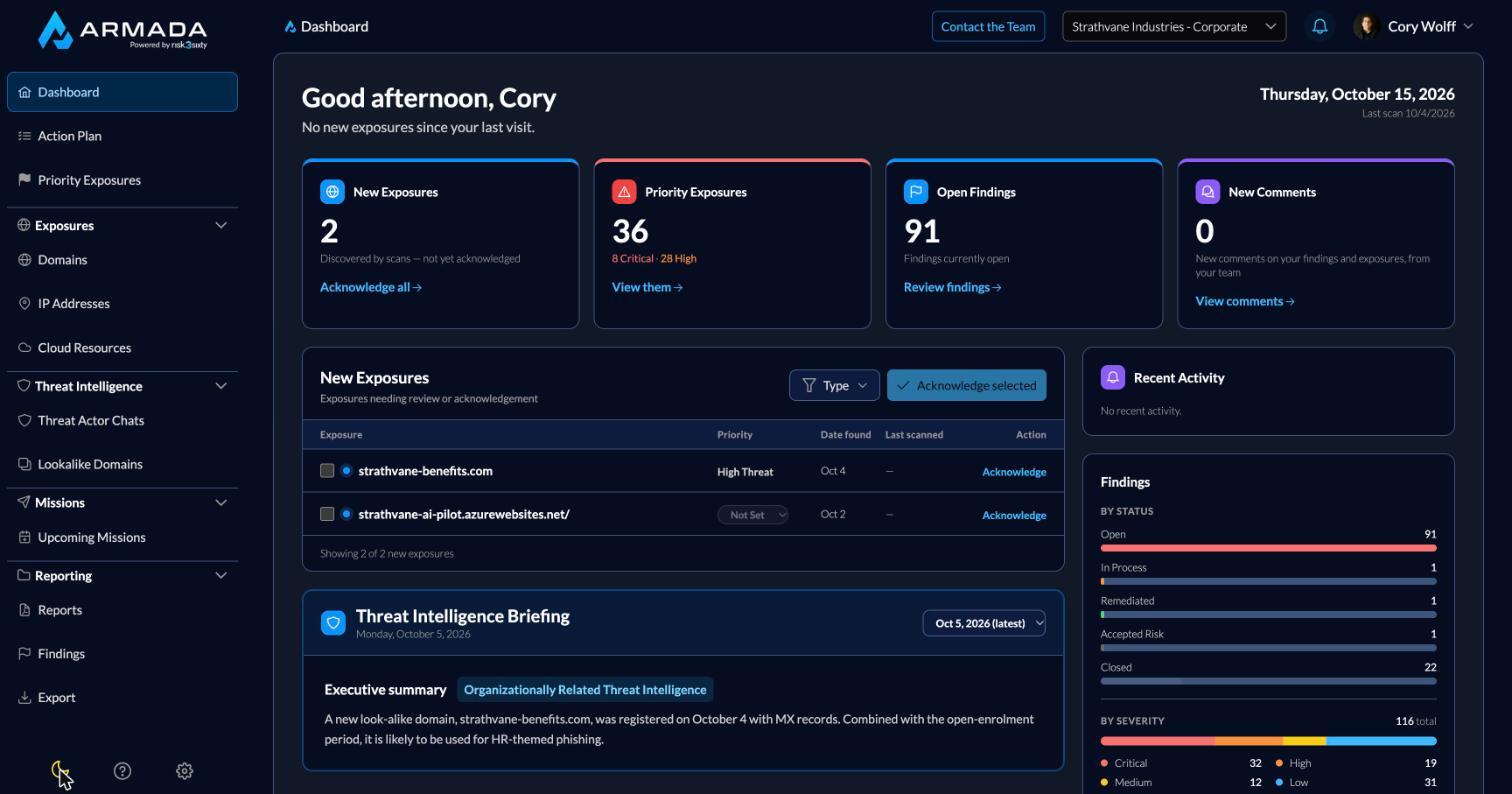
  • New exposures to acknowledge, with priority and date found
  • Findings by status and severity, from open to closed
Armada dashboard with new exposures, priority exposures, open findings, and recent activity

Fix the right things, in the right order.

Most security tools surface information well and say little about what to do with it. The action plan de-duplicates findings from every part of the platform and from tools you already run, then ranks the fixes. The result is a short list of fixes your team can actually work through.
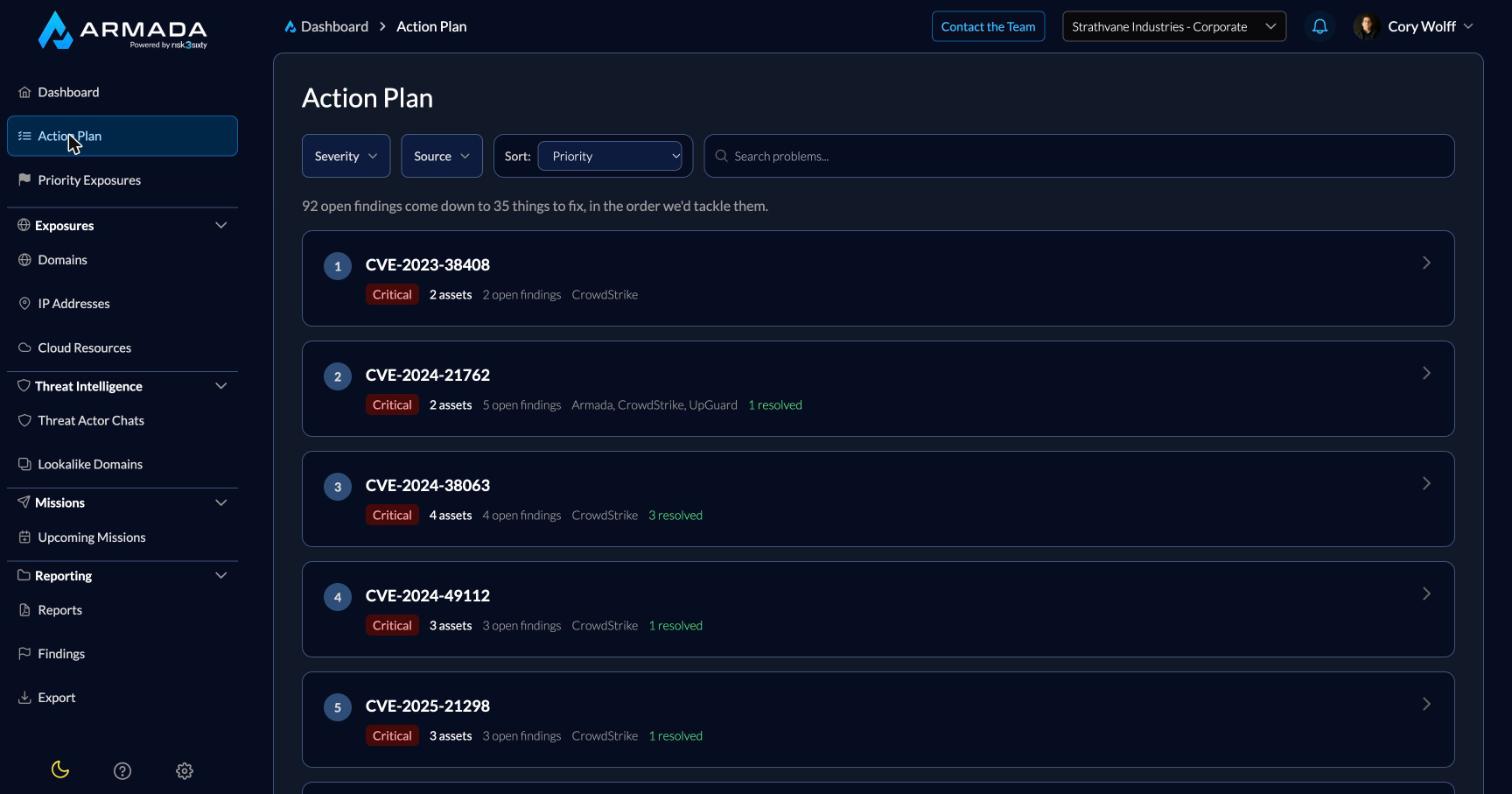
  • Ranked by attack-path impact and business context, not CVSS alone
  • Each action shows affected assets, sources and what's already resolved
  • Fixes are retested automatically and tracked to closure
Armada action plan listing numbered fixes with severity, asset counts, sources and resolved counts

See everything an attacker can see.

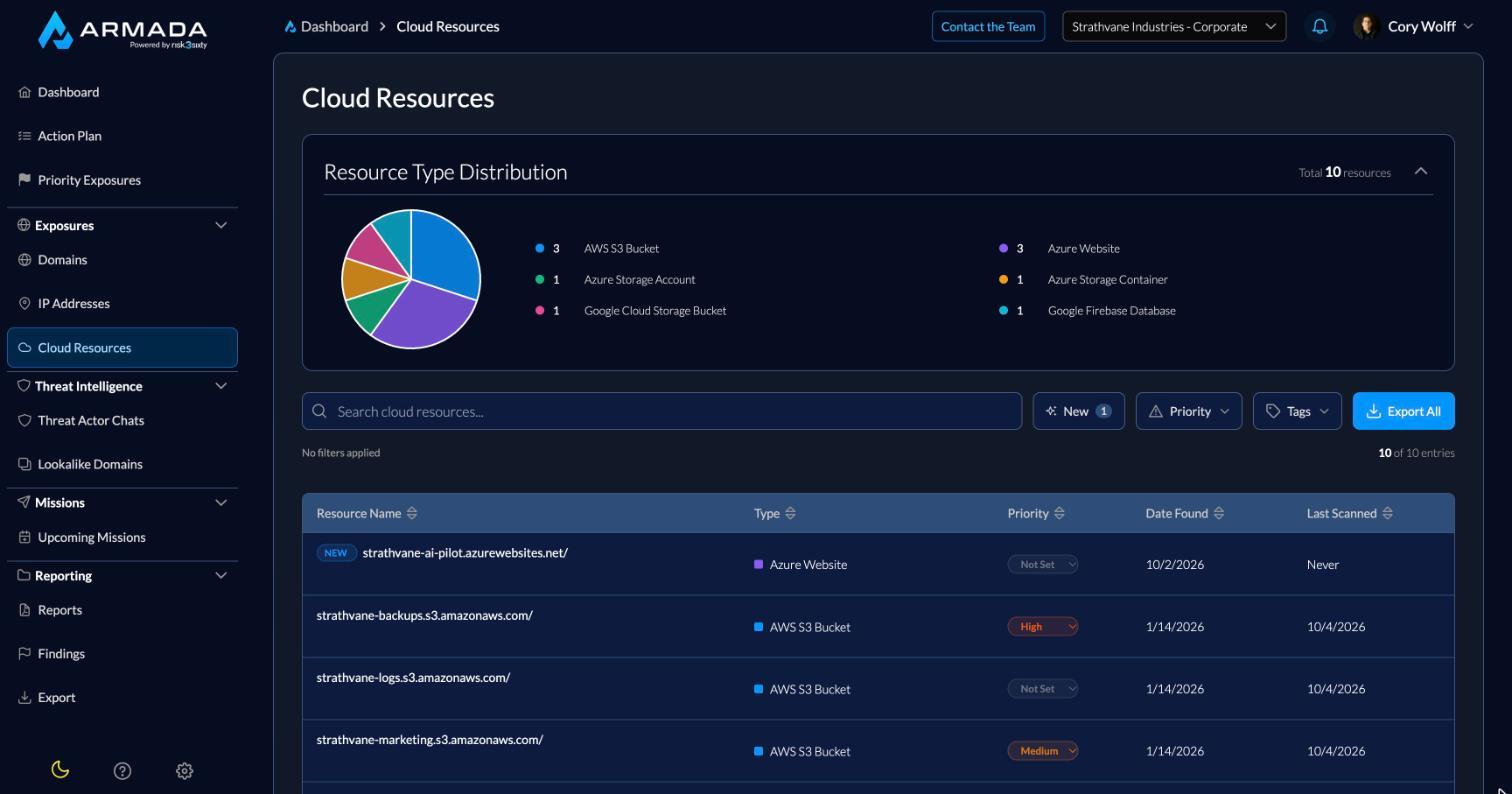
Domains, subdomains, IP addresses and cloud resources across AWS, Azure and Google Cloud, discovered continuously and reconciled to your asset map. Anything believed to be internal that is reachable from the internet is flagged.

External exposure management
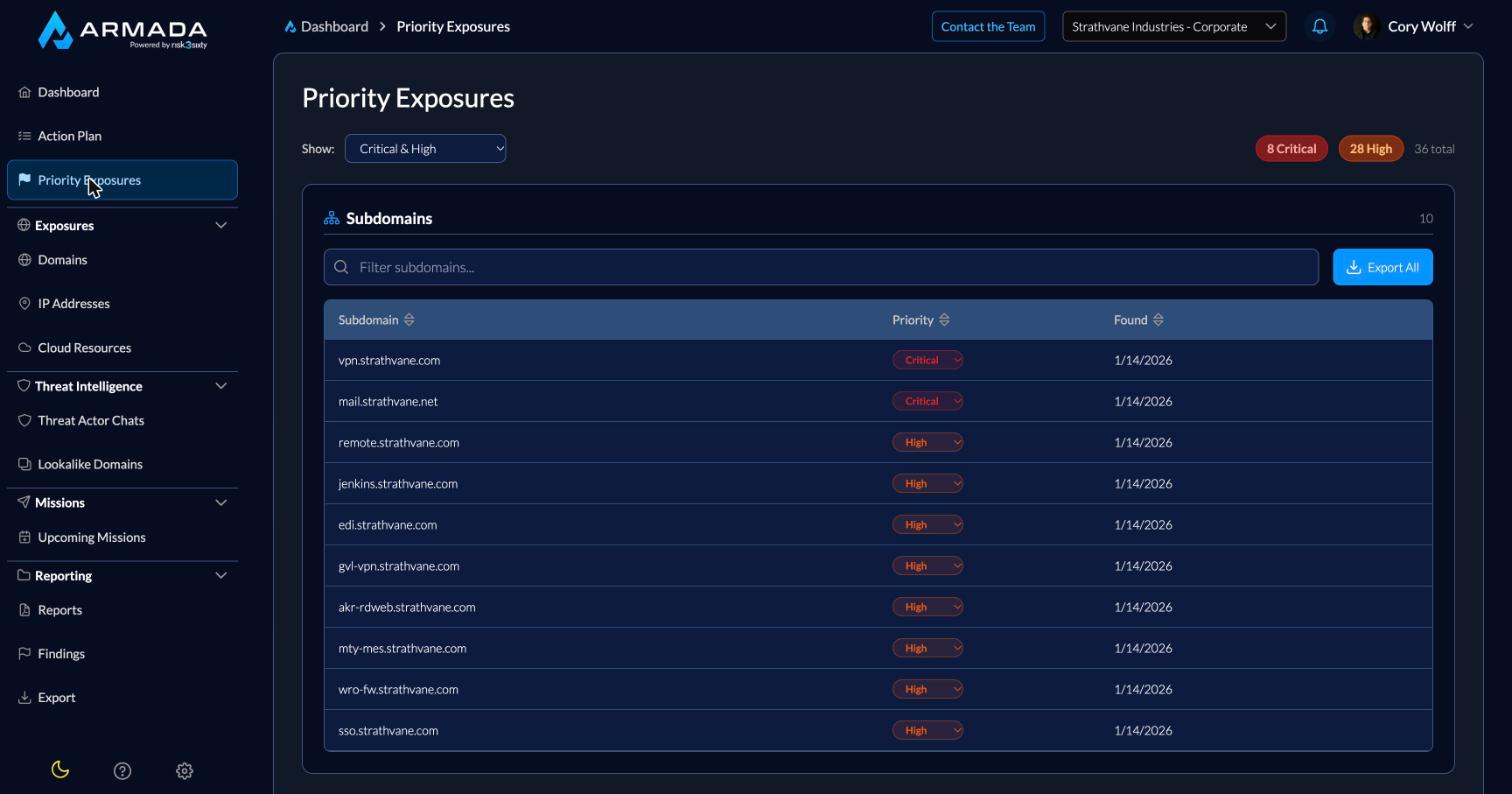
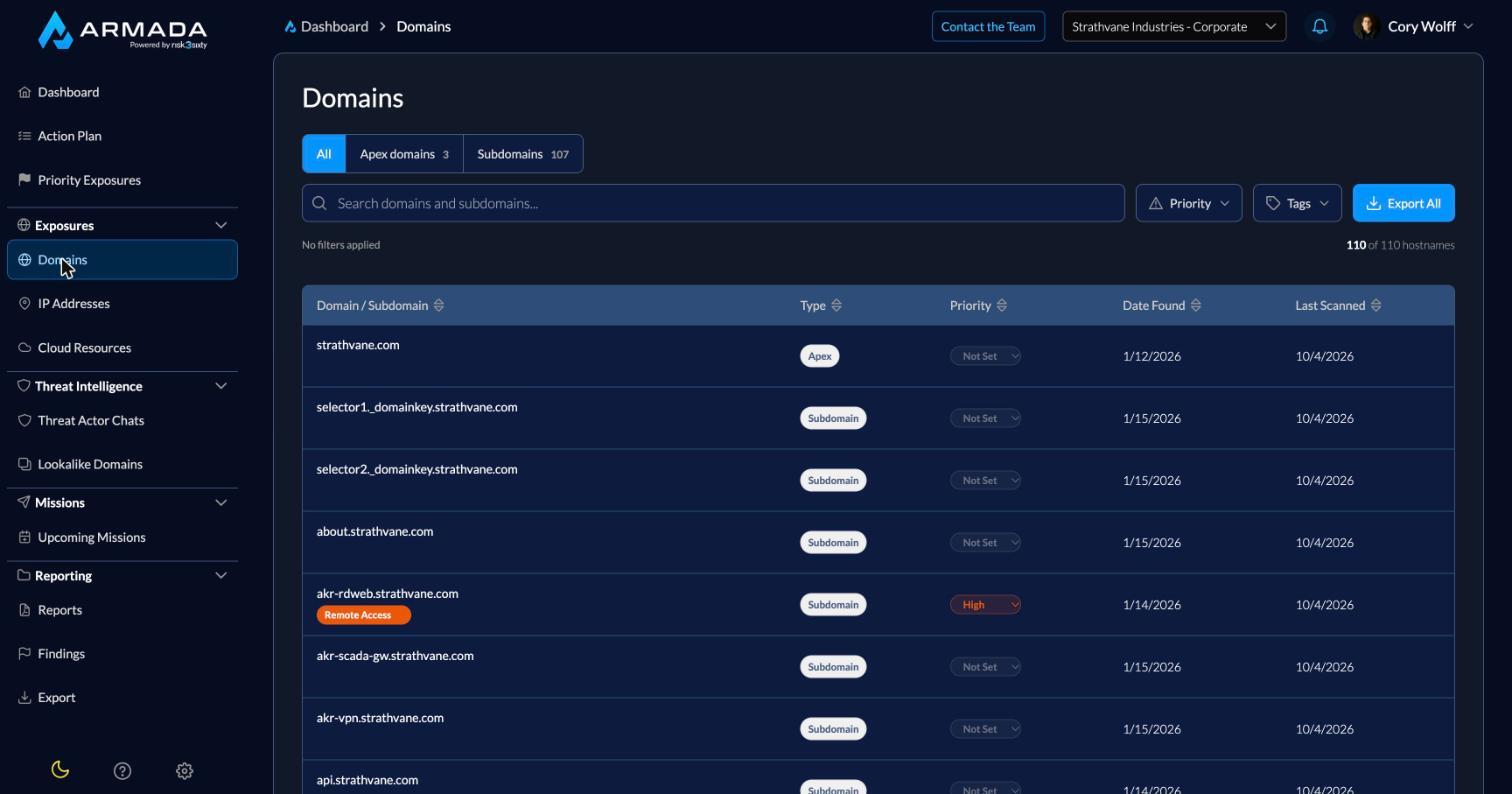
Priority exposures with 8 critical and 28 high subdomains such as VPN, mail and Jenkins hosts

Screens show sample data, not client data.

Know when someone is getting ready to use your name.

Lookalike domains, breach data and leaked credentials, monitored continuously and written up in plain language. For example, a new lookalike domain registered with mail records lines up with open enrollment, a likely setup for HR-themed phishing.
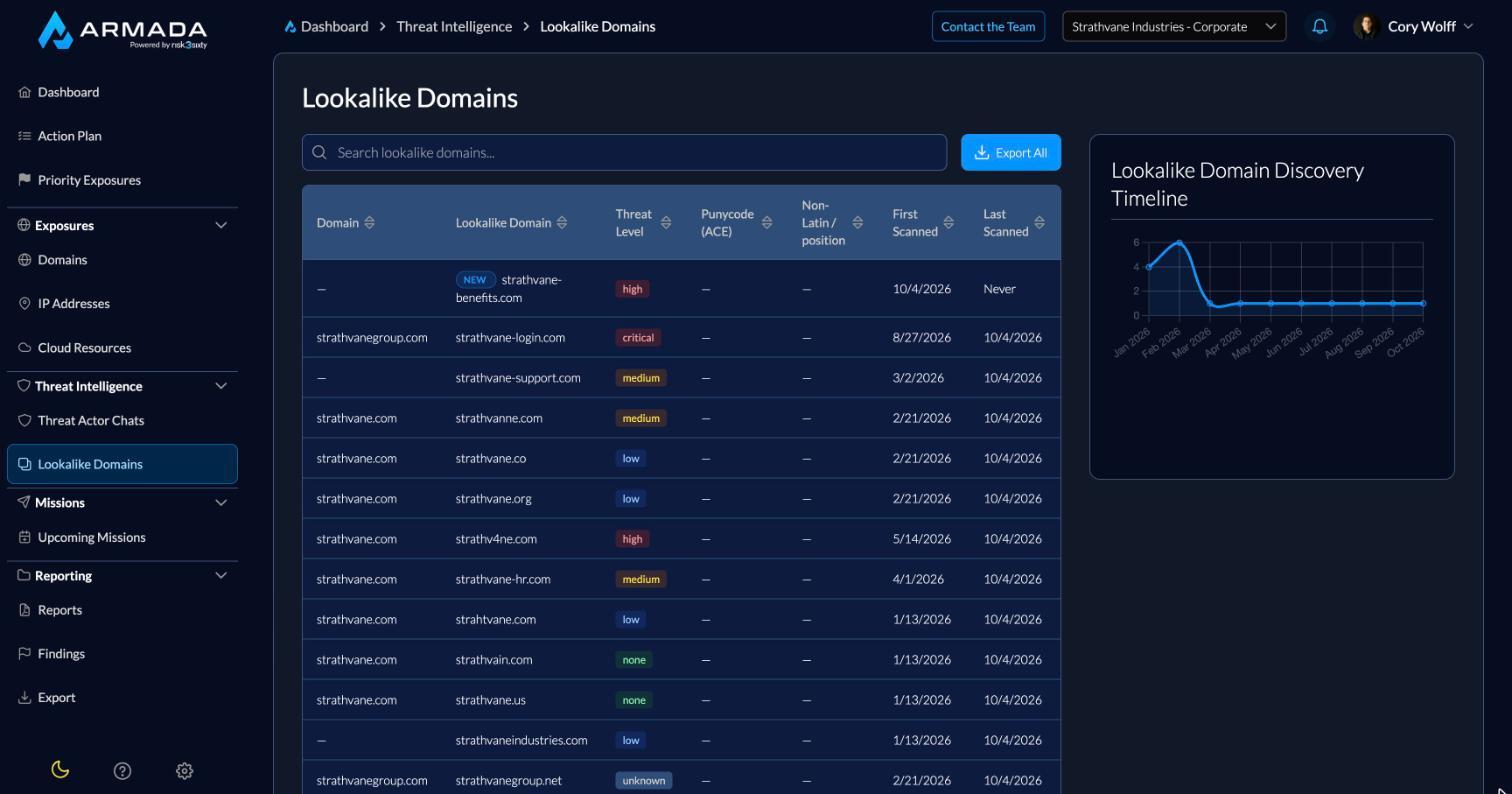
  • Lookalike and typosquat domains, scored by threat level
  • Breach data and compromised accounts tied to your people
  • A consolidated exposure baseline in month one
Lookalike domains table with threat levels and a discovery timeline chart

Fight fire with fire.

Attackers point autonomous agents at your network. Armada points them inward first, then sets traps for theirs and guards your own agents from being turned. Engagements and alerts from every agent appear in the same view as your exposures.

Corsair internal agentic testing

Armada's AI testing agent, deployed per site, network segment and trust zone. It runs reconnaissance, exploitation and lateral movement continuously, tests agents and internal MCP servers as their own asset class, and maps every technique to MITRE ATT&CK and MITRE ATLAS. Our team members validate high-impact paths.

Armada Corsair
ARMADA ACTIVE DEFENSE

Armada Deception Agents

Decoy systems, credentials and data placed where an attacker's agent will look. They adapt to how the attacker behaves, feed it false information, and page a human the moment they're touched.

Armada Deception Agents
ARMADA ACTIVE DEFENSE

Armada AI Gateway

An inline gateway between your users and agents and the models, MCP servers and tools they call. It detects and stops prompt injection, keeps agents on approved tools and connectors, and logs every call into AI usage telemetry.

Armada AI Gateway

AI usage telemetry

Activity from your teams' AI assistants, including Claude and Microsoft 365 Copilot, baselined per user and role. Alerts on usage far above baseline, regulated data in prompts, new connectors and prompt-injection indicators, routed to your SIEM.

AI usage telemetry

Works with the security tools you already run.

Connect your existing tools from the Integrations page in the platform. Their findings land in the same de-duplicated action plan as Armada's, and alerts reach your team where they already work. Credentials are stored per organization and never shared across clients.
Inbound Bring your findings in

CrowdStrike Falcon

Vulnerabilities from Falcon Spotlight become Armada findings, and external assets from Falcon Exposure Management become exposures. Syncs on a schedule, with severity and tag filters you set.

AWS Inspector

Inspector findings flow into your action plan alongside everything else, with automatic closing for findings Inspector reports as resolved.

UpGuard

UpGuard findings appear in the same ranked action plan, so third-party and attack-surface results aren't tracked in a separate tool.

Nessus scan uploads

Upload Nessus results straight into the platform. Every uploaded file is scanned for malware before it's processed.

Alerts Get alerts where you work

Slack

Connect a channel in a few clicks. Alerts for new exposures and finding status changes link straight back to the record. The Armada app installs in your workspace.

Microsoft Teams

The same alerts, delivered to the Teams channel you choose.

Email

Opt in per alert type, each with a link to the record.

In-app inbox

Every alert is always in the platform. Each user picks their own channels, so nobody gets noise they didn't ask for.

Don't see your tool? Ask us in your demo. Product names are trademarks of their respective owners.

Machines for speed. People for judgment.

Automation handles the baseline. Our CREST-accredited team members are paged when something departs from it, and they validate every high-impact finding before it drives major action.

  • A testing agent finds a viable path to administrative control or a critical asset
  • A deception agent adapts away from its baseline in response to a live attacker
  • The AI Gateway stops a prompt injection or an agent calls an unapproved tool
  • A user's AI telemetry departs sharply from their own baseline
  • A fix would disrupt the business, including removing shadow IT someone depends on

Every Armada service.

Continuous services run your program every day, and point-in-time engagements validate and deepen it. Everything feeds one action plan, so no finding ends up on a shelf.

Walk through the platform with a member of our team.

We'll show you the dashboard, the action plan and the agentic layer, then talk through what your first 90 days would surface.

Risk-free proof of concept for the Armada PlatformFree implementation and a 90-day money-back guarantee.
CREST accredited
Armada is a CREST accredited provider.Red team and penetration testing work is delivered by CREST-accredited team members.